A $30 bug detector is one diode measuring how much radio energy is nearby. It will register a strong transmitter at roughly arm’s length, and it will make a camera lens glint through its red viewport. It cannot tell a bug from your router, and it cannot find anything switched off or quietly recording to a memory card. Treat it as a close range confirmation tool, not a room sweep.
The same black plastic box sells for $27.99 and for $250.00, depending on whose name is stamped on it. EMC engineer Kenneth Wyatt bought his test units as the Ballistol K18S at $27.99 and the Raviad X13 at $39.99. The specialist retailer Jammer Store lists what appears to be the identical K18 body at $250.00 with the same claimed specification sheet. That spread is the first honest signal in this category, and nobody selling one is going to point it out.
What follows separates what these devices do from what the packaging says they do, using the only published bench measurement anyone has run on one. No affiliate links here, no picks.
What does a $30 bug detector actually do?

Tim Deagan opened one up for Make:, and the mystery collapses once you see the working principle. It is “RF peak power detection, using a diode to convert the power level of the RF signal into a voltage level.” A diode, a filter, and a row of LEDs that climb with that voltage. No receiver. No tuner.
Everything else in this article grows out of that. In Deagan’s words, the device “can’t distinguish between different frequencies, protocols, or modulation types…It only determines the overall level of RF energy.” When those teal segments climb, they are not reporting a frequency, a protocol, or a device. They are reporting that more radio energy is hitting the antenna than there was a second ago.
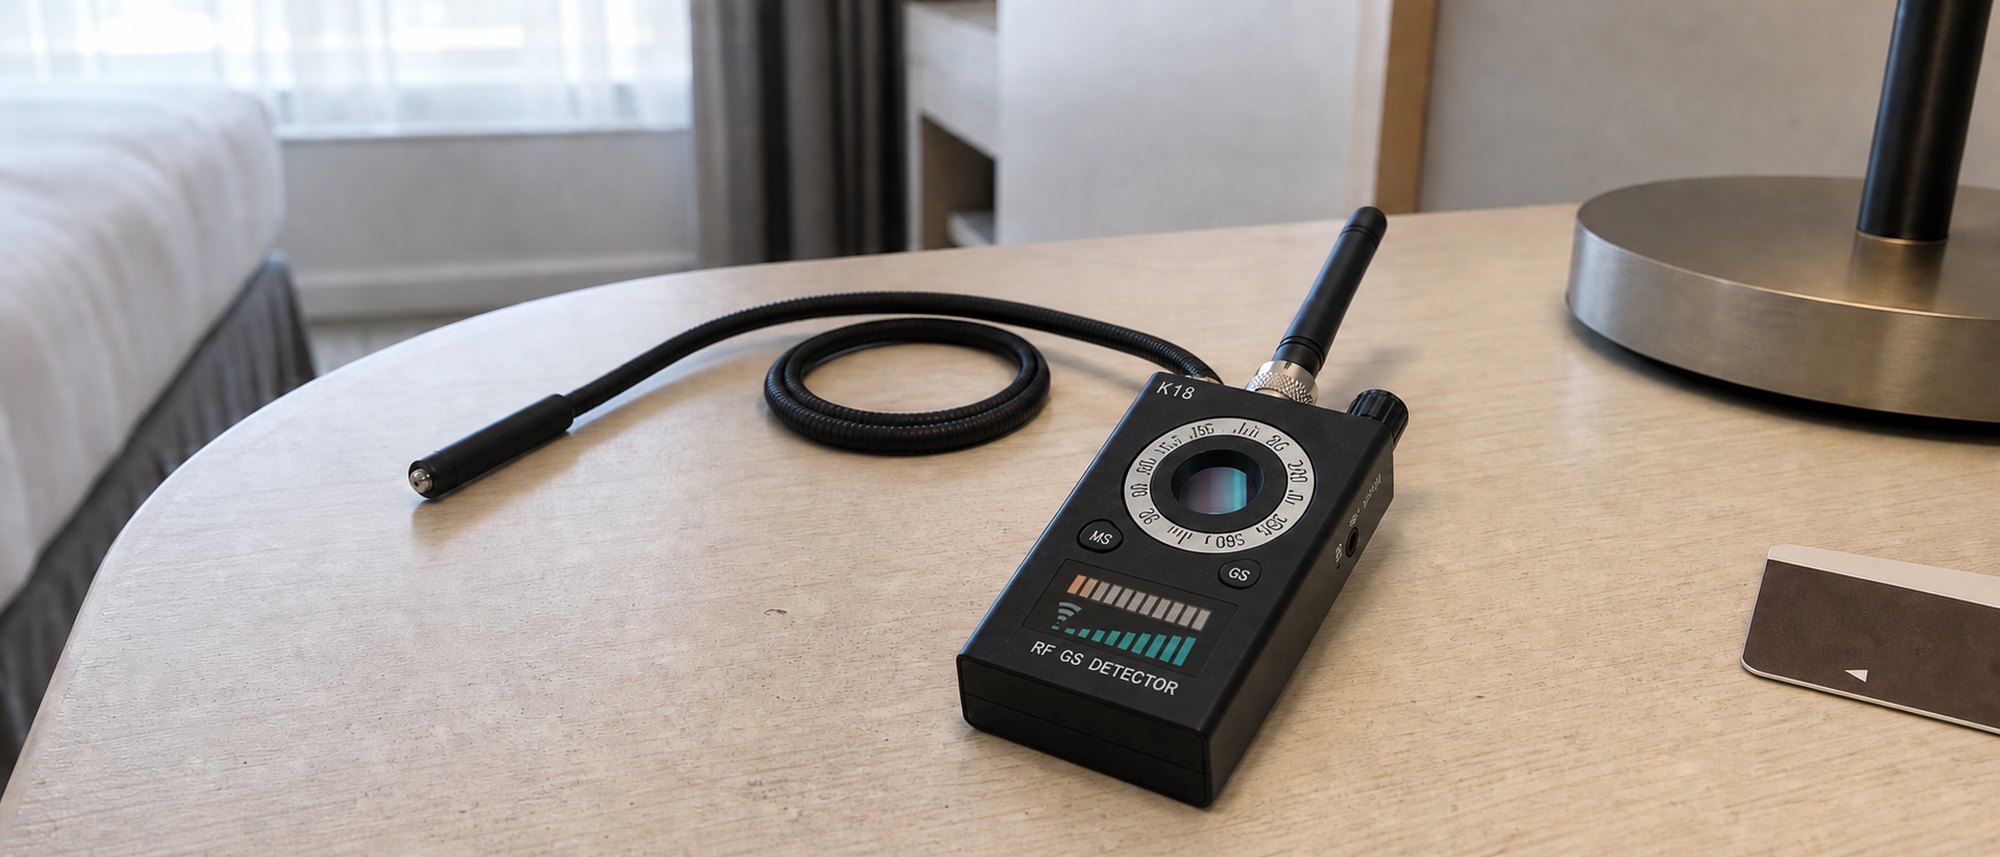
The hardware matches the modest job: a matte plastic box the size of an old pager, a stubby rubber antenna, a gooseneck probe, two buttons marked MS and GS, a red filtered viewport and a ten segment bar graph. The claim on the packaging is grander. “Wireless detecting range: 1MHz to 6.5GHz,” reads the factory listing, covering GSM, WiFi, Bluetooth, FM, VHF and UHF. The K68, a taller wand shaped cousin, raises that to 8000 MHz and adds a ten level alert. Some marketplace listings call it a “Military Version.”
What did Kenneth Wyatt’s bench test actually find?

Exactly one person appears to have put a calibrated signal into one of these and written down what came out. Kenneth Wyatt did it in January 2024 for Test & Measurement Tips, using a Red Oak Canyon RF Pro Touch generator set to +10 dBm and stepped every 10 MHz from 50 MHz to 2700 MHz.
Sensitivity came in patches rather than a range. “The most sensitive frequency ranges were 200 MHz to 600 MHz, 900 MHz to 1500 MHz, and 2000 MHz to 2700 MHz.” The second unit, the card shaped X13, “really didn’t start sensing RF until 140 MHz, but then sensed all frequencies up through 2700 MHz.” Nothing anywhere near the 1 MHz on the box. Above 2.7 GHz the sweep stopped, so the top of the advertised range is unverified rather than disproven.
Range was the bigger surprise. “The average range was 1m or less,” measured against a transmitter putting out a healthy +10 dBm. The seller specification promises detection of wireless cameras from “10cm-10m.” You are not scanning a room from the doorway. You are checking one object at a time, close enough to touch it.
The sensitivity knob turned out to be nearly binary: Wyatt found it “quite finicky in that there seemed to be a threshold level that was either ‘deaf’ below or full scale above that threshold.” Two samples, two models, one bench, so this is not a claim about every unit shipped. It is the only measured evidence there is, and it points one direction.
Why does it alert on everything in the room?

Because our homes are saturated, by regulation, in exactly the places the detector is most sensitive. The relevant rule is 47 CFR 15.247, and its title is the whole explanation: “Operation within the bands 902-928 MHz, 2400-2483.5 MHz, and 5725-5850 MHz.” WiFi lives there. Bluetooth lives there. Cordless phones, smart plugs, doorbells, thermostats. Two of those three bands sit inside Wyatt’s measured sensitivity patches, so a device with no frequency discrimination will light up in any modern home, and it will be right to.
Jimmie Mesis has worked in technical surveillance countermeasures for more than 35 years, and he is blunt about the result. Cheap RF detectors sold online, he writes at USA Bug Sweeps, “are nothing more than glorified toys,” because “that radio signal could be from a local TV or radio station, the client’s or neighbor’s Wi-Fi, a cordless phone, an active cell phone, a wireless security camera, a Bluetooth device, a SmartTV.” A sweep firm in Sydney describes the same first five minutes from the buyer’s side: “You turn the device on, and suddenly it’s beeping everywhere.”
The r/TSCM and r/privacy threads read identically. “My RF detector went off at basically everything,” one poster reported. A guest whose detector fired at outlets and air vents in a rental got the correct diagnosis from the community: “Zigbee and Z Wave both operate around 900-910 mhz in North America… It’s why a RF detector alone isn’t super useful.” Most consumer hidden cameras, meanwhile, ride the same 2.4 GHz WiFi as everything else you own, over the shared local network we walk through in how WiFi security cameras work.
Even the buying guides trip on it. Digital Camera World names the Sherry K68 its best overall pick, then concedes in its own hands on notes that the unit “still needed me, the user, to figure out false positives.” Sorting the false positives is the entire task, and the device does not help with it.
What a cheap detector can and cannot find
Here is the whole picture in one place, each answer tied to the measurement or the practitioner behind it. The middle column is what sales pages leave out.
| What you want it to do | Realistic answer | Why |
|---|---|---|
| Register a live transmitter you are standing next to | Yes, at about arm’s length | Measured average range of 1m or less against a +10 dBm source |
| Tell that signal apart from your router, phone or smart plug | No | One diode reads total RF power, with no frequency or protocol information at any stage |
| Make a camera lens glint through the red viewport | Yes, close and slow | Retroreflection sends light straight back from the sensor behind the lens |
| See a lens hidden behind black plastic or a smoked housing | No | The blinking light technique fails on enclosures like a black tissue dispenser |
| Find a camera that is switched off or recording to a card | No | RF detection needs the device to be transmitting; there is nothing to receive |
| Catch a GPS tracker or GSM bug between transmissions | Rarely | Those send brief bursts every few seconds or minutes and stay silent in between |
| Cover the advertised 1MHz to 6.5GHz | No | Bench testing found nothing near 1 MHz and verified nothing above 2.7 GHz |
| Locate a magnetically mounted tracker on a car | Only within a few centimeters | The gooseneck is a magnetic probe, not a radio; a tracker fixed without a magnet is invisible to it |
Four of those rows need more than a table cell. Mesis frames the core blind spot as a question: “what if the device is off, was remotely turned off, or it’s a recording device and doesn’t transmit a signal?” A cheap detector, he answers, “can only detect an RF bugging device if it’s on.” A regular in r/security puts it plainer: “Detecting wired or recording cameras that aren’t transmitting data is tough/impossible.”
Burst transmitters are the second hole. Wyatt notes that “most GPS trackers only transmit a brief burst of location information every few seconds (or minutes). Therefore, they are typically difficult to detect using the RF detector mode.” Murray Associates, a counterespionage firm that sells no equipment, adds GSM bugs and Bluetooth trackers to the same category: they “transmit infrequently. This makes them difficult to detect.”
The third is design: a transmitter can be built to look like nothing at all, “using spread spectrum scrambling techniques to generate noise-like signals very similar to the RF interference produced by LED lamps,” as one r/privacy commenter described it. The fourth is the one nobody expects. A buyer who tested his new K18 the sensible way, on a transmitter he could verify, reported that he “turned on my smartphone and the spy detector wouldn’t show anything, as if there was no smartphone in the room.”
Does the lens finder actually work?

Yes, and it is what keeps the category from being a pure scam. The red window is not decoration. Deagan explains the physics: “A retroreflector is a device that reflects radiation directly back at the source, regardless of the angle,” and the K18 pairs “a ring of red LEDs surrounding a viewport with a red light filter.” Put light next to your eye, aim it at a lens, and a bright dot comes straight back. Wyatt confirmed it on the bench and was not expecting to: lenses “reflect back brightly when viewed through the red-filtered viewport,” and “it surprised me just how brightly hidden camera lenses reflect.”
It also works on cameras the RF side cannot touch. A wired camera, a camera recording to a card, a camera sitting powered down but still pointed at the room: all of them still have glass in front of a sensor.
The technique is unforgiving. Deagan’s summary runs three words: “Slow, steady, and close are the key techniques,” and the thing you are hunting is “usually less than 5mm across.” Murray Associates catalogues the cost. The method is labor intensive “because lots of things reflect light,” which hands the user “a galaxy of false positives,” and it has one flat failure mode: “The blinking light technique does not work if the spy camera is hidden within a black plastic enclosure, like a tissue dispenser.” A bright flashlight held beside your eye does much the same job. Their verdict on the whole gadget tier is worth carrying while you scan: “There are no ‘totally’ effective do-it-all spy detection gadgets.” We go deeper on the physical and network side of a search in our guide to finding hidden cameras in a room you do not control.
What do professionals actually use?
This is the contrast that explains a K18’s price rather than excusing it. A professional sweep is not a better beeping box. It is a different set of instruments answering different questions.
| Capability | A $30 detector | Professional TSCM instruments |
|---|---|---|
| Spectrum coverage | Measured sensitivity in patches between 140 MHz and 2.7 GHz | The REI OSCOR Green covers 10 kHz to 24 GHz |
| What it reports | Total RF energy as a bar graph | A swept spectrum: 24 GHz in 1 second, 2,000,000 data points per second |
| Devices that are switched off | Nothing at all | Non-linear junction detection locates electronics on standby, powered down, or with a dead battery |
| What the kit costs | Street prices around $48 to $93 for the popular models | Around $50,000 for the spectrum analyzer alone, and no less than $100,000 for a working sweep kit |
The analyzer figures come from the OSCOR Green specification, an instrument built “to detect illicit eavesdropping signals, perform site surveys for communication systems, conduct radio frequency (RF) emissions analysis, and investigate misuse of the RF spectrum.” That model is now marked discontinued, so read it as a reference point for what spectrum analysis means rather than a shopping suggestion. The cost figures are Mesis’s, out of three decades of the work.
Non-linear junction detection is the capability with no consumer equivalent at any price. Murray Associates put it plainly: an NLJD “can locate spycams and other bugging devices even when they are on standby, turned off or out of battery power.” It finds semiconductor junctions rather than signals, which is why the on or off question stops mattering. A detector measuring 2.7 GHz with one diode is not a small version of an instrument that sweeps 24 GHz every second. It is a different tool wearing similar marketing.
When is a cheap detector still worth using?

There is a real use case, and it is narrower than the box implies. A cheap detector confirms a suspicion you have already localized by other means. It does not search a room for you.
Technique is most of the difference. Murray Associates found that “the best results were achieved when the device’s sensitivity was reduced and the unit was brought within three feet (preferably less) of a transmitter.” A TSCM regular on Reddit describes it as a procedure: “start in a different room, adjust gain until you stop seeing signal spike (setting the noise floor), then walk into target room and bring the detector close to each item that you are investigating.” Turn the gain down until the room goes quiet, then move in, object by object.
The pattern that justifies owning one looks like this. An r/privacy poster found their detector silent everywhere in a room except at a freshly repaired patch of drywall, and it fired on both sides of the wall: “The detector goes off when held up to the patch of wall that was repaired. Everything else in the room doesn’t set off anything.” A repeatable, localized reading that lines up with physical evidence is worth following. The community’s next step was right and free: kill the breakers and see whether the reading survives.
Two rules matter more than the hardware. A beeping bar graph is not evidence of surveillance; radio energy is everywhere, and a reading says nothing about who put it there. A quiet scan is not a clean bill of health either, because the devices that worry people most are the ones that stay silent.
So finish with your eyes and hands instead of the LEDs. Wyatt’s confirmation step on a suspect object is physical: “examine it closely on the back or bottom. You’ll likely find a micro SD card slot somewhere.” At home, your router’s client list tells you more than the bar graph does. If you do find a real device, leave it in place and call the police rather than handling it or confronting anyone, and read where you stand in the laws on hidden cameras in a home.
If what you have is a $30 box and a bad feeling, it can still help you check one drawer, one smoke alarm, one vent. Its job is narrowing a search you already started. Handing it a whole room is what makes it look like a toy. More teardowns of consumer security gear live in the Security Tech section.
Sources
- Test & Measurement Tips: Kenneth Wyatt, review of electronic bug and hidden camera detectors, January 2024, the bench measurements used throughout.
- Make: Tim Deagan, how to detect spy tech, on diode power detection and retroreflection.
- USA Bug Sweeps: Jimmie Mesis, bug sweeps, detection or deception.
- USA Bug Sweeps: cheap bug sweeps versus professional TSCM sweeps.
- Murray Associates: spy camera detectors, on lens finders and their limits.
- Murray Associates: TSCM technology, on non-linear junction detection and infrequent transmitters.
- Electronic Code of Federal Regulations: 47 CFR 15.247, operation within the 902-928 MHz, 2400-2483.5 MHz and 5725-5850 MHz bands.
- REI OSCOR Green specification, listed as discontinued, accessed August 10, 2026.
- Factory listing for the K18 signal detector, source of the claimed specification text and the reference photographs.
- Jammer Store: K18 bug detector listing at $250.00, claimed frequency range and detection distances.
- SpyProWorld: K68 detector specification, claimed 1 MHz to 8000 MHz range, battery and alert levels.
- Digital Camera World: best hidden camera detector, 2026, for current street prices and its own false positive caveat.
- Bug Sweep in Sydney: why cheap bug detectors do not work, April 2026.
- r/TSCM: false positives and correct RF detector setup.
- r/privacy: rental detector alerts explained as Zigbee and Z Wave traffic.
- r/privacy: the repaired drywall patch case.
- r/privacy: a new K18 that failed to register a smartphone, April 2026.
- r/privacy: on spread spectrum signals designed to look like interference.
- r/security: on detecting wired and recording only cameras.